
If your application uses open-source code, it means that you are relying on components you didn’t write and can’t fully control, including the vulnerabilities coming with that code.
This is where you should consider using Software Composition Analysis (SCA) tools, which scan your dependencies and catch any hidden security issues or risky licenses before they cause problems.
Below, we will offer some of the top Software Composition Analysis Tools that you can consider for your development workflows. And before we start reviewing them one by one, here is a quick comparison table with features and pricing info included.
Features | Pricing | Best for | |
| Aikido Security |
|
| Individual developers, startups, and growing teams |
| Snyk |
|
| Individual developers and development teams |
| Socket Security |
|
| Individual developers and growing teams |
| Checkmarx |
| Custom quote | Developers and AppSec teams |
1. Aikido Security

Aikido Security is a unified security platform that also provides software composition analysis solutions. It works by scanning your open source code dependencies and identifying any common vulnerabilities and exposures (CVEs). It also flags malware, license, and EOL issues, so you can fix them before they cause security or legal issues.
It stands out among other SCA tools for its reachability analysis, where instead of simply reporting a vulnerability, it traces whether your code actually calls the vulnerable part of that library.
Key features
- Reachability + Exploitation analysis
- Full software visibility with SBOMs
- SCA integrated across your entire SDLC
- Vulnerability protection with Aikido Intel
Pricing
- Standard Pentest: The pricing starts at $4000 per assessment
- Aikido Platform: Starts at $350/month (up to 10 users). A free plan is also available for up to 2 users.
Best for: Individual developers, startups and growing teams
2. Snyk

Snyk Open Source is a security management tool that helps developers find, prioritize, and fix open source security vulnerabilities and license issues. You can find vulnerabilities while coding in your IDE or CLI, add security guardrails to your CI/CD pipelines, and test your production environment for existing vulnerabilities.
Key features
- Remediation prioritization based on the risk level
- Fast fixing to reduce exposure
- Continuous monitoring
- Open source management automation
Pricing
Individual developers can start with Snyk for free, while bigger teams can subscribe to the pricing plans offering more functionality, starting at $25/month per contributing developer.
Best for: Individual developers and development teams
3. Socket Security

Socket Security’s SCA solutions scan open source dependencies for both known vulnerabilities (CVEs) and suspicious code behavior, catching malicious packages and zero-day supply chain attacks. It easily integrates into CI/CD pipelines and also scans and enforces open source license policies, helping teams stay compliant while protecting against a broader range of supply chain threats.
Key features
- Protection against zero-day supply chain attacks
- Vulnerability scanning (CVE's)
- Open source dependency visibility
- Dependency optimization tools
- Best-in-class open source license scanner
- Configurable license enforcement policy
- Integrations for all your favorite tools
Pricing
Socket Security also offers a free plan for individual developers to test its features. The paid plans start at $25 /per month /per developer.
Best for: Individual developers and growing teams
4. Checkmax

Checkmarx SCA scans your open source dependencies to find vulnerabilities, malicious packages, and license risks. It uses reachability analysis to prioritize only the issues that could actually be triggered in your running app. It integrates into your IDE, CLI, and CI/CD tools and gives prioritized remediation guidance for fixing what matters most.
Key features
- SCA scan accuracy
- Deep dependency scanning
- Malicious package protection
- Reachability analysis
- Actionable remediation guidance
- Policy automation
- License risk management
- SBOM
Pricing
Checkmarx offers a custom quote based on the models that match your attack surface.
Best for: Developers and AppSec teams
So, What is the Final Pick?
Open source code is a fast move in software development, but they also come with vulnerability and license risks. Modern SCA tools help you address these issues and fix them before it is too late.
By doing so, choose Aikido Security for its advanced reachability analysis, Snyk for remediation prioritization features, Socket Security for scanning existing and potential vulnerabilities, and Checkmarx for SBOM generation and management.
Related Blogs
.png)
What Is an Anti Detect Browser — and Why Does It Matter in 2026?Every time you open a browser, you broadcast a fingerprint. Not your IP address — something far more specific: your canvas hash, WebGL output, installed fonts, screen resolution, timezone, audio context, and dozens of other signals that websites use to identify you as a unique device.Standard browsers send this fingerprint[…]
Are you managing multiple accounts on Facebook, Google, or Amazon but constantly getting banned due to "duplicate IP" or "fingerprint detected"? This is a common problem that thousands of marketers and sellers face every day. And the solution that more and more experts are turning to is the antidetect browser.So what is an antidetect browser, how does it work, and who should use it? This article[…]
Agility in business used to mean fast reactions—responding quickly to change. Today, agility means anticipation: the ability to see patterns before they unfold and act with precision. Yet this level of awareness can't come from instinct alone. It comes from data—and more importantly, from how that data moves between people, processes, and decisions.A CRM app may reveal customer behavior, but[…]
Digital marketing today runs on speed and volume. Brands are expected to push out fresh creatives constantly, and traditional video production simply can’t keep up. That’s where an AI Facebook ad generator comes in. These tools take product links, scripts, or raw assets and turn them into ready-to-use Facebook video ads with minimal manual editing. 1. Pollo AI Pollo AI works as a practical AI […]

Captcha is a popular security tool used on websites to prevent suspicious activities from automated programs (bots). However, Captcha can sometimes be frustrating for users, especially when fast access is needed or when the Captcha becomes overly complex. In this article, we will explore 7 effective ways to bypass Captcha in 2025, allowing you to overcome these barriers legally and safely.1. What[…]
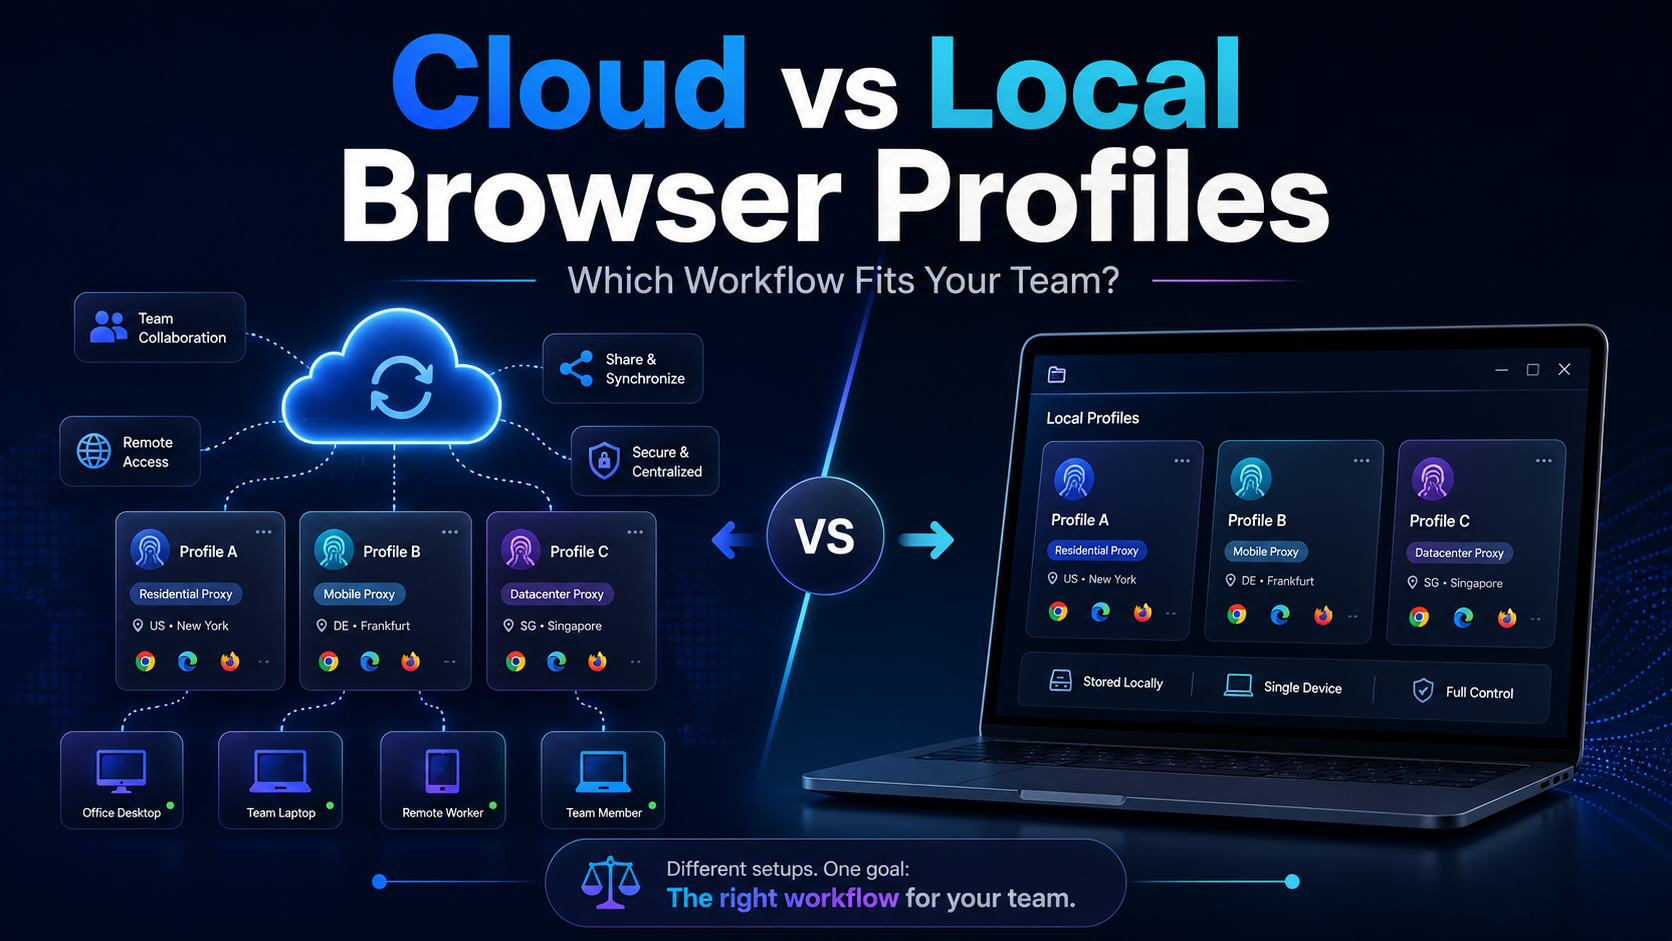
Cloud vs Local Browser Profiles: Which Workflow Fits Your Team?When a team starts managing multiple browser profiles, one of the most important decisions is whether to use cloud profiles or local profiles.Local profiles can be attractive because profile data is primarily stored and operated on the user's device, providing more direct control and reducing reliance on synchronization. Cloud[…]
