.png)

Every time a user accesses a website, a host of tracking mechanisms are silently at work — from collecting device information to creating browser fingerprints, even when they use incognito mode or a VPN. This is no longer a hypothesis, but a reality of the modern web.
In the context of increasing user concerns about personal data and tightening regulations such as the General Data Protection Regulation (GDPR), privacy has become a crucial factor in building trust. A website needs to be not only fast and aesthetically pleasing, but also transparent and secure.
Therefore, building products with a "privacy-first" approach is no longer an option, but a competitive advantage. Businesses that are ahead of this trend—combining it with tools such as Hidemium — This will create more opportunities to gain user trust in the long term.
1. What is Browser Fingerprinting? Things Developers Need to Understand
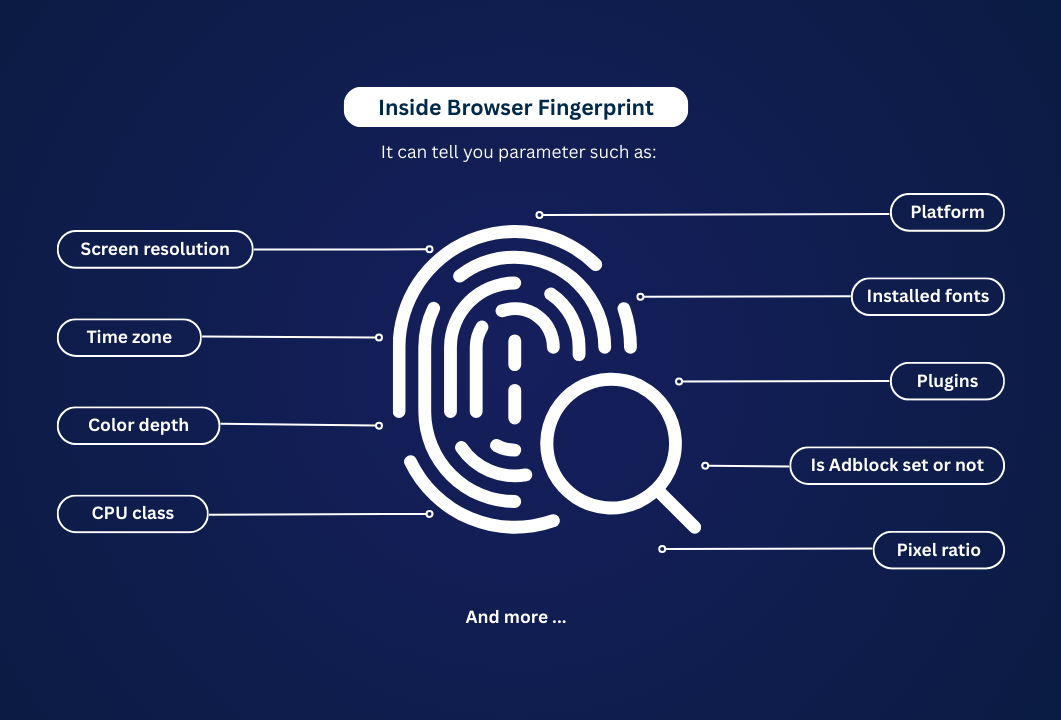
Before building a privacy-protecting website, you need to understand how modern tracking systems work. One of the most common techniques today isbrowser fingerprinting— A method for creating a “digital fingerprint” based on information from the user’s device and browser.
Unlike cookies, fingerprints are not stored on the user's device and therefore cannot be manually deleted. Instead, each time a system accesses a location, it recreates this identifier based on the same set of signals from the hardware, software, and access environment. This makes tracking much more persistent and difficult to avoid.
The data collected is often spread across multiple layers. At the hardware level, the system can identify the GPU, CPU core count, RAM capacity, or screen resolution. At the software level, it records the operating system, browser version, plugins, and fonts. Additionally, there are network signals such as IP address, time zone, language, and even WebRTC leaks. Finally, there are rendering signatures like Canvas, WebGL, or AudioContext—factors that help increase the accuracy of device identification.
Individual data points may seem insignificant, but when combined, they form a nearly unique "digital signature" for each user. Numerous studies have shown that this method can identify returning users with very high accuracy, even when they have attempted to remain anonymous.
This is especially important for developers. Because if your website integrates third-party scripts—such as analytics tools, advertising, or social media plugins—there's a high chance fingerprinting has already occurred, even before the user has given consent according to the General Data Protection Regulation.
Therefore, more and more users are seeking ways to minimize tracking using solutions such as VPNs, proxies, or advanced anonymity tools like Hidemium. Understanding how these technologies work also helps you—as a developer—build more transparent and privacy-respecting products.
>>> Learn more: Top 15 Reliable Free Proxy Websites
2. Website architecture that prioritizes privacy: Core principles
Building websites in the anti-tracking era can't just stop at adding cookie banners. Instead, privacy needs to be integrated right from the system design stage. Today, web development companies play a crucial role in shaping how responsibly user data is handled, as they are often the ones architecting these digital experiences from the ground up. Below are the key principles that developers and businesses need to apply if they want to build a sustainable and trustworthy platform.
2.1 Strictly control third-party scripts
A typical website can load dozens of third-party scripts, and each script has the potential to become a point of user data collection. Therefore, the first step in "privacy-first" development is to review all external resources: which scripts are truly necessary, and which can be replaced with a self-hosted or more privacy-friendly solution.
More importantly, this isn't a one-time task. As the website updates or integrates new features, the risks increase. Developers need to maintain continuous control and monitoring throughout the product lifecycle.
2.2 Properly Implementing a Content Security Policy (CSP)
One of the most effective forms of protection available today isContent Security Policy (CSP)— A mechanism that allows you to precisely control the resources that the browser is allowed to load. This helps prevent unwanted scripts, even if they are injected through security vulnerabilities.
However, simply enabling CSP isn't enough. If the configuration is too tight, the website may experience functional errors; if it's too loose, it's almost ineffective. Setting up an effective CSP requires practical experience and a thorough understanding of the system architecture being used.
2.3 Switch to a privacy-friendly analytics system
Many websites still rely on traditional analytics tools, which are capable of collecting user data at a deep level. Instead, solutions like Plausible, Fathom, or Matomo (self-hosted) provide sufficient data without cookies or sharing information with third parties.
The transition to these platforms not only leads to better compliance with regulations such as the General Data Protection Regulation, but also provides an opportunity to streamline the measurement system—focusing on truly important metrics instead of collecting indiscriminate data.
2.4 Authentication Security and Session Management
Login systems are one of the most data-sensitive areas. A privacy-focused architecture needs to ensure standards such as using HTTP-only cookies to protect sessions, limiting token lifespan, supporting multi-factor authentication, and having a logout mechanism that truly terminates the session.
Furthermore, user data should be encrypted and stored only at the minimum necessary level. This is not only a security best practice, but also a mandatory requirement for compliance with legal regulations.
2.5 Prioritize server-side and minimize data
Applications that rely heavily on client-side processing (especially large JavaScript frameworks) often expose more signals to fingerprinting mechanisms. Therefore, in many cases, using server-side rendering or static generation will help reduce the data collection surface.
In parallel, the principledata minimizationThis also needs to be implemented thoroughly. Websites should only collect what is necessary for their defined purpose. Every form field, every event tracking, or every pixel needs careful consideration before implementation — not only for performance, but also for user trust.
>>> Learn more:What is a Residential Proxy? A Tool for Ensuring Online Privacy and Identity Protection
3. Why can't businesses ignore privacy-first web development?
Many businesses still view privacy as merely a "tick-checkbox" to comply with, rather than a strategic element. However, in today's context, this approach is not only outdated but also carries significant costs and risks.
First, legal pressure is increasing. Regulations like the General Data Protection Regulation are no longer just warnings but are being strictly enforced, with fines potentially reaching tens of millions of euros. Violations such as collecting data without consent, improper processing of information, or a lack of adequate security measures are all on the priority list for enforcement. This means that a website not designed with privacy protection in mind from the outset can become a direct legal risk for a business.
Besides legal factors, user trust also significantly impacts business performance. When users feel unsafe—from slow website loading times due to excessive scripts to signs of excessive data collection—they tend to leave before taking any action. Conversely, a minimalist, transparent, and privacy-respecting website not only provides a better user experience but also naturally increases conversion rates.
For B2B businesses, this standard is even higher. Business clients often evaluate websites as part of their partner vetting process. A platform lacking basic security signals, using unclear tracking, or not properly managing data can damage credibility from the very first contact.
In summary, privacy-focused web development isn't an expense, but a long-term investment. It helps businesses mitigate legal risks, build trust, and optimize conversion rates—factors that will become increasingly important in the future.
>>> Learn more: 3 ways to use a proxy to bypass firewalls effectively and safely.
4. What should you look for in a privacy-prioritizing web development partner?
Building a website with a "privacy-first" approach isn't just about choosing the right tools; it requires a team with in-depth knowledge of both technical aspects and regulations, such as the General Data Protection Regulation. When evaluating partners, you should focus on the following factors:
Experienced in implementing GDPR compliance systems and possessing a thorough understanding of data protection requirements in markets such as the EU or UK.
There is a rigorous process for testing and controlling third-party scripts, including their configurability.Content Security Policy (CSP) effective
Understanding authentication security, including session management, tokens, and user data protection mechanisms.
Experienced in deploying privacy-friendly analytics platforms instead of relying entirely on traditional tracking tools.
Providing long-term support helps maintain security and privacy standards throughout the website's lifecycle, not just during the launch phase.
A good development partner not only delivers a stable, functional website, but also helps you build a reliable, compliant platform capable of sustainable growth in an increasingly privacy-conscious digital environment.
>>> Learn more: What is SEO Proxy? Top 5 Best SEO Proxy Providers in 2025
5. Practical steps to get started today
If your website isn't already built with privacy in mind, making changes might sound drastic. But you don't need to do everything at once—just start with these foundational steps:
Check all resources currently loading on the website.
Use browser tools like Blacklight or DevTools to see which third-party scripts and resources your website is calling when it loads. This is a crucial step in getting a clear picture of your current "tracking surface."Review the cookie consent mechanism.
A system that complies with the General Data Protection Regulation must ensure that tracking scripts are not run without the user's explicit consent. At the same time, the privacy policy needs to be transparent about the types of data collected and how they are used.Re-evaluate the security of the authentication system.
Check how you store sessions/tokens, their expiration times, and logout mechanisms. If you're storing tokens in localStorage, using long-term sessions, or not completely disabling sessions upon logout, these are areas that need immediate improvement.Conduct a technical audit regarding privacy.
A thorough audit by an experienced team will help you identify specific gaps and develop a clear improvement roadmap. This is the step that moves from "knowing the problem" to "solving it completely."
>>> Learn more: A guide to quickly and effectively disabling proxies on all browsers.
6. Conclusion: Building websites for today's users.
Browser fingerprinting and other forms of invasive tracking are no longer "behind-the-scenes technical issues" but have become a direct part of the user experience. How a website collects and processes data now directly impacts the level of trust visitors place in the brand. Businesses that proactively build a transparent platform and respect privacy will have an advantage that marketing alone cannot easily compensate for.
Developing websites with a "privacy-first" approach is not simple. It requires a combination of secure architecture, optimized frontend, compliance with regulations such as the General Data Protection Regulation, and long-term system maintenance. However, in return, it provides a solid foundation of user trust, conversion performance, and legal security.
If your business wants to build a website that's suitable for the anti-tracking era, choosing the right development partner is the most important first step. Combined with privacy-enhancing solutions like Hidemium, you'll not only create a well-functioning website, but also build a trustworthy and sustainable digital ecosystem.
Related Blogs

In the context of Surfinite no longer meeting security and automation needs well, many users are turning to more effective alternatives. 2025, Antidetect Browser Hidemium emerges as an option worth considering thanks to its capabilities hidden IP address, anti-tracking, cross-platform support, and AI automation. The article below will Hidemium detailed review – from interface to features to[…]

What is Expressvpn? This is one of the keywords that users are most interested in today, especially in the context of the increasing need to protect personal data and access the Internet without limits. Express VPN is a famous virtual private network (VPN) service that allows users to personal information security and Bypass Geo-Restrictions. Let's Antidetect Browser Hidemium Express VPN detailed[…]
In the process of doing business online, many sellers face the problem of accounts being repeatedly suspended even though their content does not violate any rules and their ads fully comply with platform policies. This leads to business disruptions, declining revenue, and major difficulties in scaling operations. The root cause lies in poor digital identity management.That is why more and more[…]
How to Change MAC Address on Mac: Complete Privacy GuideIn today's hyper-connected world, protecting your digital identity has never been more important. Every time your Mac connects to a network, it broadcasts a unique hardware identifier that can be logged, tracked, and used to build a profile of your behavior. If you've ever wondered how to change MAC address on Mac, you're not alone — it's[…]

Advantages of using PIA S5 Proxy with HidemiumGlobal coverage: Covering 200+ countries/regions around the world, over 350 million pure residential IPs, making it easy to bypass regional restrictions.Efficient management: Hidemium simplifies the proxy management process, allowing you to easily switch and manage multiple IPs.Fast connection: PIA S5 Proxy has over 99.99% high-speed connection, and[…]
One of my recent Instagram comment tests looked like an amazing deal for about thirty seconds. I ordered 10 comments from a service, and 25 appeared under the post almost immediately.Lucky me? Not quite.There were only 10 distinct texts in the entire delivery. Several had been posted multiple times by different accounts—some three times, some four. What initially looked like a generous bonus was[…]
